NIST CSF 2.0 is here: The finalized framework that made governance the center of cybersecurity
In February 2024, NIST released the finished Cybersecurity Framework 2.0, the first major update in a decade. The new Govern function moved governance from an afterthought to the hub of the whole framework. Here is what changed and why it matters.
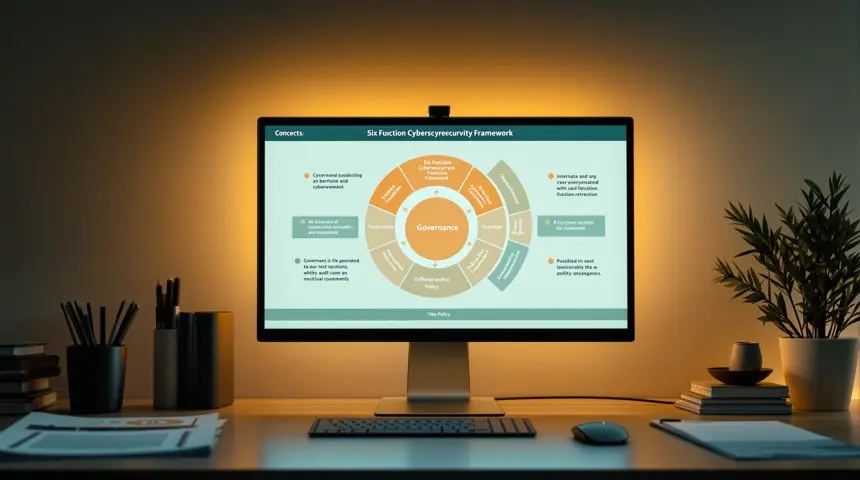
For a decade, the NIST Cybersecurity Framework was the most widely used guide to managing cyber risk in the United States and far beyond, built around five familiar functions: Identify, Protect, Detect, Respond, and Recover. In February 2024, NIST released the finished version 2.0, the framework's first major revision since 2014, and it changed the architecture in a meaningful way. The headline was a sixth function, Govern, placed not at the end of the list but at the center of the whole framework. Here is what the finalized update delivered and why the elevation of governance was the most consequential part of it.
From five functions to six
The addition of Govern was more than a new label. NIST positioned the function at the hub of the framework, with Identify, Protect, Detect, Respond, and Recover arranged around it. Govern covers the organizational context of cybersecurity: establishing the risk management strategy, defining roles and responsibilities, setting policy, and overseeing the program at the executive and board level. The visual and conceptual message was unmistakable: governance is not one activity among many, it is the foundation on which everything else rests. A security program without clear ownership and leadership engagement, the framework now argued, was incomplete by definition.
What the Govern function actually asks for
Govern is sometimes mistaken for a documentation exercise, a set of policies to write and file away. The framework's intent is the opposite. The function asks organizations to establish a risk management strategy that aligns with the business, define and communicate roles and responsibilities clearly, and ensure that leadership understands and oversees cyber risk. In practice, that means a named owner with real authority, a board or executive team that is genuinely engaged, and a decision-making process that is real rather than ceremonial. Policies matter, but only as the written expression of accountability that already exists.
Broadened scope beyond critical infrastructure
A second significant change was scope. The original framework was developed for critical infrastructure, but it had long outgrown that origin, adopted voluntarily by organizations of every size and sector. Version 2.0 acknowledged this explicitly, reframing the framework as a resource for all organizations and sharpening its language to be more practical and broadly applicable. This mattered because most of the economy, the small and mid-sized businesses that make up the overwhelming majority of organizations, had been using the framework informally for years. Version 2.0 simply made that welcome official.
Where training and awareness sit
Training and awareness have always been a core control within the Protect function, and version 2.0 kept that emphasis while strengthening its connection to Govern. The logic is straightforward: governance only works if the people carrying out the program understand it, and that understanding comes from training and communication. A security-aware workforce is not a peripheral nice-to-have but a foundational control, and the responsibility for ensuring it lies with leadership, not just the security team. Under the finalized framework, documented training became both a protective measure and an expression of governance itself.
Supply chain came into sharper focus
The finalized framework also deepened its treatment of supply chain risk, a direct response to the hard lessons of SolarWinds, Log4Shell, and the xz backdoor that would follow only weeks later. The message was that an organization's security depends on the vendors, services, and open source components it relies on, and that supply chain risk is a standing part of risk management rather than a separate, optional add-on. Version 2.0 wove these considerations through the functions, making clear that organizations need to understand and manage the risk that enters through their dependencies.
Why the finalized version mattered
NIST CSF 2.0 did not invent new controls so much as it reorganized and clarified what good security already looked like, and it did so at a moment when regulators, insurers, and auditors were increasingly referencing the framework. The elevation of governance aligned NIST with a broader shift toward accountability that was playing out in the SEC's disclosure rules and Europe's NIS2 directive. Organizations that aligned with the framework, documenting their governance and training, found themselves positioned for the expectations that were converging across the industry. The framework's direction was no longer a preview, it was the new baseline, and 2024 was the year that baseline became official.
Related reading
All articles
Written by
The Simple Training Center Team
We build and run Simple Training Center. These articles come from our work making compliance and security training practical for small and mid-size teams. No guest posts, no fluff.
More from the teamPut it into practice
Reading is step one. Training is what keeps you compliant.
Turn these insights into action. Our role-based security training takes minutes to set up and gives every learner a verifiable certificate of completion.