NIST SP 800-207: How zero trust went from buzzword to federal blueprint in 2020
In August 2020, NIST published SP 800-207, the first authoritative definition of zero trust architecture. It turned a vendor buzzword into a concrete framework, and here is what the standard actually says and why it mattered.
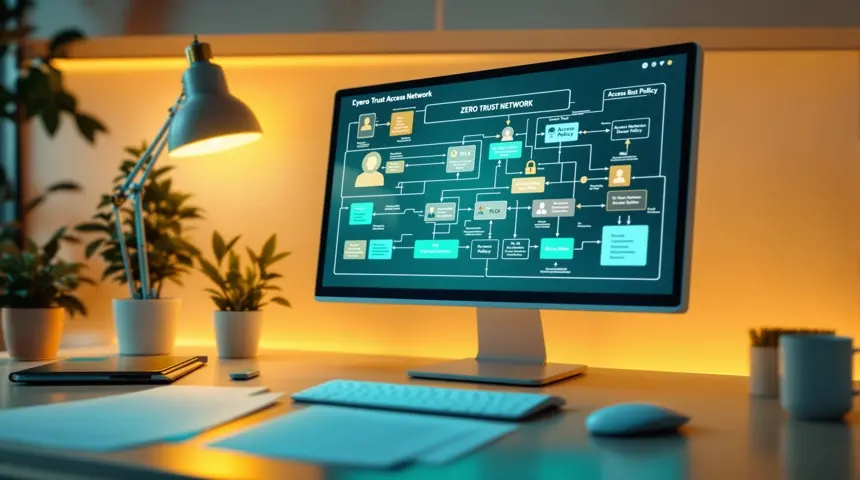
For years, zero trust was a term that vendors used liberally and defined loosely. It meant whatever the marketing department needed it to mean, and its popularity as a buzzword far outstripped any shared understanding of what it actually was. In August 2020, that changed. The National Institute of Standards and Technology published Special Publication 800-207, Zero Trust Architecture, the first authoritative definition of the concept from a neutral, rigorous source. The publication did not invent zero trust, but it gave it a concrete shape, and in doing so it set the direction for how organizations would think about security for years to come. Here is what the standard actually says.
What zero trust actually means
At its core, zero trust is built on a simple principle: never trust, always verify. No user, device, or network is trusted by default, regardless of whether it is inside or outside the organizational perimeter. Every request for access is authenticated, authorized, and validated before it is granted. This is a direct rejection of the traditional perimeter model, which assumed that anything inside the firewall was trustworthy. NIST SP 800-207 formalized this principle and provided a framework for building systems around it, rather than treating it as a slogan.
The assumptions the standard is built on
NIST SP 800-207 rests on a set of explicit assumptions that reflect the reality of modern networks. The network is assumed to be hostile, with no implicit trust in any location. Resources are accessed over connections that cannot be assumed secure. Users and devices are not inherently trustworthy, and their access must be evaluated continuously, not just at login. And the enterprise does not fully control every device or network its users touch. These assumptions, once stated plainly, made clear why the old model had failed and why a new one was necessary.
From concept to architecture
The most valuable contribution of SP 800-207 was moving zero trust from a vague idea to a working architecture. It described the components of a zero trust system: the policy engine that makes access decisions, the policy administrator that enforces them, and the policy enforcement points that sit in front of resources. It explained how these components work together to evaluate every request against policy, using signals about the user, the device, and the context. This gave organizations a blueprint to build against, rather than a slogan to repeat.
The human element in a zero trust world
Zero trust is often discussed as a purely technical shift, but people remain central to it. Under a zero trust model, employees are asked to verify their identity more often, and access is granted based on continuous evaluation rather than a single login. This requires employees to understand why the extra steps exist and to follow them consistently. Security awareness training had to evolve to cover these concepts, helping employees understand that more frequent verification is not an inconvenience but the point, and that the person is a critical part of the access decision. A zero trust architecture only works if the people using it understand their role.
Why the standard mattered beyond government
NIST SP 800-207 was written for federal systems, but its influence spread far wider. Because the federal government is an enormous buyer of technology and a standard-setter for the industry, its definition of zero trust quickly became the de facto definition everywhere. Vendors aligned their products with it, security teams adopted its language, and other organizations, including insurance underwriters and auditors, began referencing it. The publication took a concept that had been vague and vendor-driven and made it a neutral, authoritative standard that everyone could build against.
A direction, not a destination
SP 800-207 was clear that zero trust is a journey, not a product. It is not something an organization buys or installs in a weekend, but an architecture and a strategy built incrementally over time. The standard provided the map, but the actual transition, enforcing strong authentication, moving to least-privilege access, and continuously evaluating every request, was work that would take years. What the standard gave organizations in 2020 was something they had been missing: a clear, shared destination to move toward, and a common language for the journey.
Related reading
All articles
Written by
The Simple Training Center Team
We build and run Simple Training Center. These articles come from our work making compliance and security training practical for small and mid-size teams. No guest posts, no fluff.
More from the teamPut it into practice
Reading is step one. Training is what keeps you compliant.
Turn these insights into action. Our role-based security training takes minutes to set up and gives every learner a verifiable certificate of completion.